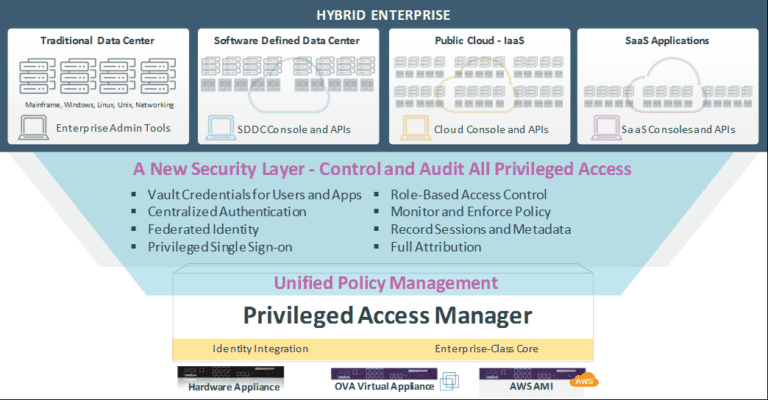
PAM Provides the Following Core Capabilities:
-
Granular Policy Enforcement
Policy enforcement separates high-risk users using integrated Java applets with reverse port tunnelling, isolating critical IT infrastructure components and supporting segregation of duties for compliance. Symantec LeapFrog Prevention™ restricts users within these segments using allowlists and blocklists, preventing movement outside authorised areas at the socket level.
-
User Activity Monitoring
User activity monitoring tracks actions and provides real-time alerts about attempted policy violations. Administrators are promptly informed when access violations are attempted, detected or prevented. Access can be terminated if a user attempts to reach an unauthorised system or device.
-
User Event Recording
User event recording centralises activity tracking through session recording and playback. Administrators can review user actions in CLI sessions. Recording can be configured by user profile or endpoint. Command-line activity is monitored, recorded and archived for audit and compliance.
-
Centralised Reporting
Centralised reporting provides comprehensive, tailored audit and compliance reports for all user-initiated events. Reports can include usage data and attempted security breaches. You can also run automated reports focused on individual users' compliance, schedule them at predefined intervals and distribute them by email.
PAM Provides the Following Additional Capabilities:
-
Secrets Management
Policy enforcement separates high-risk users using integrated Java applets with reverse port tunnelling, isolating critical IT infrastructure components and supporting segregation of duties for compliance. Symantec LeapFrog Prevention™ restricts users within these segments using allowlists and blocklists, preventing movement outside authorised areas at the socket level.
-
Host-Based Device Access Control (Unified PAM Server Control)
User activity monitoring tracks actions and provides real-time alerts about attempted policy violations. Administrators are promptly informed when access violations are attempted, detected or prevented. Access can be terminated if a user attempts to reach an unauthorised system or device.
-
Threat Analysis
User event recording centralises activity tracking through session recording and playback. Administrators can review user actions in CLI sessions. Recording can be configured by user profile or endpoint. Command-line activity is monitored, recorded and archived for audit and compliance.