HCL AppScan on Cloud is a fully hosted and managed cloud application security subscription that helps protect your organisation's business and data. Using SAST, DAST, IAST and SCA, it detects common vulnerabilities across web, mobile and open-source applications.

A Comprehensive Cloud Application Security Testing Suite

Static, dynamic, interactive and open-source application security testing in one place. HCL AppScan on Cloud offers a complete suite of technologies for broad coverage of web, mobile and open-source applications.

  • Dynamic Analysis (DAST)
  • Static Analysis (SAST)
  • Interactive Analysis (IAST)
  • Software Composition Analysis (SCA)
looks_one

Web API Scanning

Expand vulnerability coverage by automatically scanning web APIs using Postman collections, OpenAPI descriptions, recorded traffic or HCL AppScan's integration with leading API testing tools.

looks_two

Incremental Scanning and Test Optimisation

Save time and resources with incremental scanning, limiting tests to new code or areas containing issues identified in earlier scans. Use the test optimisation slider to balance coverage and scan speed across the SDLC with four optimisation levels. Choose scanning that is 10 times faster at 70% accuracy, or twice as fast at 97% accuracy. The choice is yours!

looks_3

Action-Based Scanning and Login Management

Use the embedded browser to explore the application as a user would, providing a user-centric rather than traditional traffic-based view. Browsing and authentication actions can be recorded using the built-in recorder or Activity Recorder browser extension and replayed to exercise application logic more accurately. Advanced capabilities support one-time passwords and third-party authentication.

looks_4

Detecting Vulnerable Third-Party Components

Attackers target known vulnerabilities in popular libraries that may be included in your application. Combining DAST with vulnerable third-party component detection provides broader coverage, identifying libraries with known vulnerabilities and showing those findings alongside DAST results.

looks_5

OWASP Top 10 & OWASP API Security Top 10

The OWASP Foundation leads community-driven open-source projects that research and provide application security guidance. HCL AppScan DAST technology helps us offer 100% coverage of the most common vulnerabilities and security risks in both major benchmarks.

Minimise the risk of data breaches and malicious attacks with dynamic analysis. Our DAST technology scans running applications and APIs for vulnerabilities during development, before they reach production.

Integrating automated DAST at any development stage helps you assess complex applications and risks, and manage and resolve vulnerabilities before deployment to the web.
  • User-Defined Tests
    Create custom rules to identify specific application issues or errors. Inspect traffic for unwanted content or behaviour, build payloads and look for reflected behaviour indicating a problem. External servers can also be used to verify known blind attacks.
  • Multistep Operations
    Recorded and action-based multistep operations let you test complex application logic sequences. If a series of actions is needed to bring a page into a particular state before testing, the sequence can be replayed to establish that state.
looks_one

The Industry's Broadest Programming Language Coverage

HCL AppScan SAST supports more than 30 programming languages, providing broad access to source code security testing across technology environments. Whether you work with legacy code or modern frameworks, it strengthens and streamlines secure coding practices, making it a leading choice for developers worldwide.

looks_two

Integrate Anywhere

Integration is essential to a smooth, efficient development lifecycle. HCL SAST tools connect easily with leading CI/CD platforms, IDEs, defect tracking systems and other DevOps tools, including Visual Studio, GitHub, GitLab, Jenkins, ServiceNow, Azure DevOps and Jira. This integration supports a unified workflow for rapid development without compromising security, making HCL SAST a valuable part of modern development teams' toolsets.

looks_3

AI-Driven Scan Accuracy with IFA 2.0

Improve scan accuracy with IFA 2.0 (Intelligent Finding Analytics), which uses AI to reduce your workload. It handles much of the triage by automatically filtering out 98% of false positives and grouping remaining findings into remediation groups that can be addressed with a fix at a single point in the code.

looks_4

Broader Scan Coverage with AI

HCL AppScan SAST uses AI and machine learning through Intelligent Code Analytics (ICA) to expand scan coverage. ICA automatically discovers new APIs, reviews third-party APIs and frameworks, and assesses their security impact.

looks_5

Secrets Scanning

Our SAST technology can identify confidential data, credentials, social security numbers and API keys that developers accidentally commit to source repositories. Finding and removing secrets is critical to software supply chain security, as malicious actors may steal or use them to compromise applications further.

Analyse application source code and data flows to find coding and design flaws that indicate security vulnerabilities, so you can address issues before releasing the software.

Improve application security by testing code early in the SDLC with Static Application Security Testing (SAST). Developers can identify source code vulnerabilities accurately and integrate security into development through IDEs and CI/CD pipelines. SAST helps detect and address vulnerabilities before they become security risks.

  • Automatic Remediation
    Alongside SAST scanning, HCL AppScan CodeSweep provides automatic remediation for vulnerabilities detected in an IDE. Currently, more than 50% of CodeSweep findings can be fixed automatically. The existing GitHub integration will also add automatic remediation by creating pull requests containing proposed fixes.
  • Remediation Recommendations
    HCL AppScan SAST provides effective remediation guidance by identifying vulnerabilities and common design flaws in code. Alongside alerts, SAST generates and recommends one or more fixes and supports resolution through the continuously updated HCL AppScan Security Knowledgebase.
looks_one

API Discovery

HCL AppScan IAST automatically detects and catalogues internal APIs used by an application. Additional information is available from SCA scans of the open-source packages used to develop those APIs. These findings are essential to understanding security risk and reporting it to the relevant stakeholders.

looks_two

Automatic Issue Correlation

HCL AppScan Auto Issue Correlation extracts data from each IAST, DAST and SAST issue and applies heuristics to identify relationships. By grouping issues that can be resolved together, it reduces the overall number of vulnerabilities and remediation tasks. DAST findings can be enriched with details from corresponding IAST and SAST scans that have source code visibility. SAST findings can be prioritised using the accuracy of matching IAST and DAST results. SAST fixes can be verified by subsequent IAST and DAST scans that update the status of all correlated findings.

looks_3

Patented Java Solution

Our patented Java deployment solution requires less configuration and setup time because IAST can be deployed as a Java agent or a web application. You can start scanning sooner, deploy IAST after the web server has started and remove the agent without restarting the server. The agent also detects, downloads and installs its own updates automatically (ASoC only).

looks_4

Patented .NET Solution

Our patented .NET IAST deployment solution is the fastest on the market and runs in managed rather than native code. There is no need to disable core .NET optimisations. Because the IAST agent runs as part of the .NET code itself, it provides access to more capabilities and helps identify more types of issues.

looks_5

Eliminating False Positives

HCL AppScan IAST also holds patents for advanced algorithms that track information flowing through an application. Detected vulnerabilities trigger additional checks to reduce false positives in the final report. These algorithms replicate code flows in real time and test them in different ways. If you implement effective custom sanitisation code, HCL AppScan IAST recognises it and does not report issues in flows protected by that code.

Monitor all activity interacting with your code at runtime, legitimate or malicious, to identify vulnerabilities that need remediation.

Integrate security into the software development lifecycle with Interactive Application Security Testing (IAST). It actively monitors running applications and APIs to identify and address vulnerabilities quickly. Its source code visibility improves the accuracy and depth of issue identification.

IAST operates autonomously during functional or quality testing. It can also work with DevOps and security teams, intelligently correlating scan results with DAST and SAST findings to group issues for rapid remediation.

looks_one

Cloud Security Through Container Scanning

HCL AppScan has developed container scanning that uses Software Composition Analysis (SCA) to inspect all the content of a Docker container or image without running it.

looks_two

Software Supply Chain Security

Strengthening software supply chain security is essential to protecting your business. HCL AppScan SCA detects open-source packages, versions, licences and vulnerabilities, providing an inventory for comprehensive reporting.

looks_3

Source Code Scanning

HCL AppScan maintains its own database of open-source and third-party packages, used by our SCA tool to improve source code scanning. SCA identifies and analyses software packages and compares them with the database using file hashes, binaries and other information. An automated process gathers information and monitors new vulnerabilities to keep the database up to date daily. Sources include NVD, GitHub Advisory and Microsoft MSRC, as well as less widely known security advisories and open-source issue trackers.

looks_4

A Complete Solution with SCA and SAST

HCL AppScan SCA can run automatically alongside HCL AppScan SAST, enabling simultaneous vulnerability testing of proprietary code and third-party components.

looks_5

SCA Throughout the SDLC

HCL AppScan SCA integrates at many points in the application development lifecycle. Developers can assess open-source packages directly from their IDE. Security and release managers can use CLI and graphical tools to evaluate components in a folder or container image and identify open-source packages. Extensive plugins support other pipeline integration points, while the HCL AppScan REST API enables further integration and automation.

Identify open-source libraries and components in your code by analysing information from sources such as file hashes and binaries.

Protect applications against critical vulnerabilities introduced by open-source components with Software Composition Analysis (SCA). Our SCA technology uses a continuously updated database to identify vulnerabilities associated with these components.

HCL AppScan SCA integrates into different stages of the application lifecycle, enabling security teams, release managers and others to evaluate components within folders or container images quickly. This helps identify packages with known vulnerabilities or potential licensing issues.

Benefits of HCL AppScan on Cloud

dashboard
Centralised Dashboard

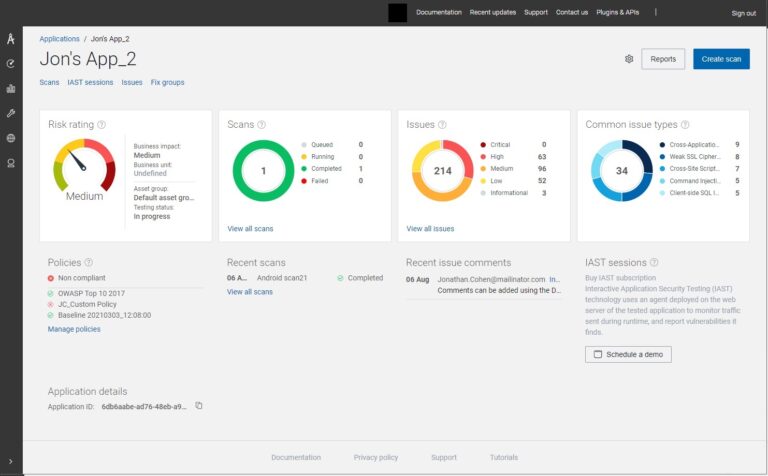
A customisable dashboard brings all test results, testing status and remediation progress together in one place.

policy
Customisable Policies

A broad range of customisable security, industry and regulatory policies enables security teams to manage priorities while testing earlier in development.

info
Actionable Reporting

Remediation recommendations for each vulnerability simplify and accelerate triage and resolution.

assured_workload
Legal Compliance

Meet industry standards and benchmarks such as PCI DSS, HIPAA, OWASP Top 10, SANS 25 and more.

beenhere
Always Up-to-Date Information

Continuous updates keep testing current and help detect the latest vulnerabilities and attack vectors.

Would You Like to Know More About HCL AppScan on Cloud?

Our Customers

CATTA Consulting
CATTA Consulting
CATTA Consulting
CATTA Consulting
CATTA Consulting